Building and maintaining an in-house Security Operations Centre (SOC) requires substantial investment, a team of hard-to-find security analysts, and round-the-clock staffing. For most UK businesses, this is neither practical nor cost-effective. That is why outsourced SOC—also known as SOC as a Service—has become the preferred approach to enterprise-grade cybersecurity.
Building a SOC is hard
See how an outsourced security operations centre protects you without the overhead.
What is a Security Operations Centre (SOC)?
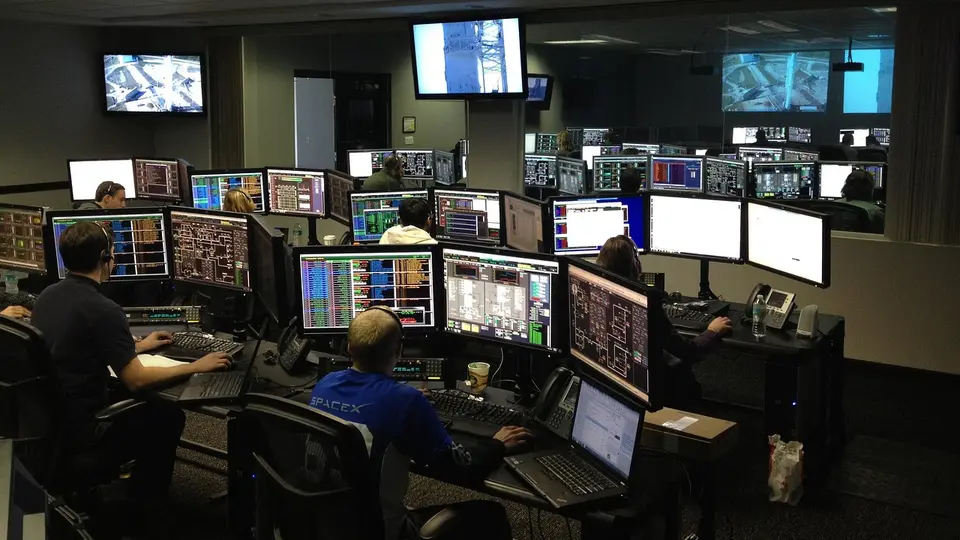
A Security Operations Centre (SOC) is a centralised facility where cybersecurity professionals monitor, detect, analyse, and respond to security threats 24 hours a day, 7 days a week. The SOC acts as the nerve centre of an organisations security operations, providing:
- Continuous threat monitoring across all IT systems
- Real-time threat detection using advanced analytics
- Incident investigation and forensic analysis
- Rapid incident response to contain threats
- Threat intelligence to anticipate emerging attacks
- Security reporting for compliance and governance
The Challenge of Building an In-House SOC
Creating an internal SOC is a significant undertaking. Consider the requirements:
Staffing Costs
A functional 24/7 SOC requires at minimum:
- 5-7 security analysts for round-the-clock coverage
- SOC manager to oversee operations
- Threat intelligence analyst for research
- Incident response specialists for containment
Staffing a SOC around the clock means a full rota of salaried specialists, plus cover for holidays, sickness, training and staff turnover.
Technology Investment
A SOC requires sophisticated technology:
- SIEM (Security Information and Event Management) platform
- EDR/XDR endpoint and extended detection tools
- Threat intelligence feeds and platforms
- SOAR (Security Orchestration, Automation, and Response)
- Network monitoring and analysis tools
Each of these tools carries ongoing licensing, maintenance and tuning effort.
The Skills Shortage
ISC2's annual workforce research has put the global shortfall of cybersecurity professionals at around four million. Finding qualified SOC analysts—let alone retaining them—is extremely challenging. Many organisations struggle to fill positions for months, leaving critical security gaps.
What is Outsourced SOC (SOC as a Service)?
Outsourced SOC, also called SOC as a Service or managed SOC, delivers all the capabilities of an in-house security operations centre through a third-party provider. Instead of building your own SOC, you leverage the providers existing infrastructure, technology, and expert staff.
Key Benefits of Outsourced SOC
1. Immediate 24/7 Coverage
From day one, you have round-the-clock security monitoring. No recruiting delays, no training periods—just immediate protection from certified security professionals.
2. Significant Cost Savings
Outsourced SOC replaces recruitment, salaries and tooling with a predictable monthly fee, which for most small and medium businesses is far lower than building the same capability in-house.
3. Access to Elite Security Talent
Top SOC providers employ highly skilled analysts with certifications like CISSP, CISM, CEH, and GIAC. You get access to expertise that would be nearly impossible to recruit directly.
4. Latest Technology and Threat Intelligence
Providers continuously invest in cutting-edge security technology and threat intelligence. You benefit from these investments without the capital expenditure.
5. Scalability
As your business grows, your security coverage scales with you. No need to hire additional staff or purchase more technology—your provider handles capacity.
6. Reduced Alert Fatigue
SOC analysts filter thousands of daily alerts, investigating genuine threats and dismissing false positives. Your team receives only actionable intelligence, not overwhelming noise.
Security operations, handled
Our team provides the SOC capability this article describes, without the hiring.
What Does an Outsourced SOC Actually Do?
A quality outsourced SOC provides comprehensive security operations:
Continuous Monitoring
Security analysts monitor your environment 24/7/365, watching for:
- Suspicious login attempts and credential abuse
- Malware infections and ransomware deployment
- Data exfiltration attempts
- Lateral movement within your network
- Cloud security incidents
- Email-based attacks and phishing
Threat Detection
Using advanced analytics, machine learning, and behavioural analysis, the SOC identifies threats that evade traditional security tools. This includes:
- Zero-day exploits
- Advanced persistent threats (APTs)
- Insider threats
- Living-off-the-land attacks
Incident Response
When threats are detected, the SOC takes immediate action:
- Containment: Isolating affected systems to prevent spread
- Investigation: Determining scope and impact
- Remediation: Removing threats and restoring systems
- Reporting: Documenting incidents for compliance and learning
Proactive Threat Hunting
Beyond reactive monitoring, SOC analysts proactively search for indicators of compromise—finding attackers who may have evaded detection.
Outsourced SOC vs In-House SOC: Comparison
| Factor | In-House SOC | Outsourced SOC |
|---|---|---|
| Setup Time | Many months | Typically weeks |
| 24/7 Coverage | Requires a full analyst rota | Included |
| Expertise Level | Limited by hiring | Specialist team |
| Technology | Capital investment | Included in service |
| Scalability | Requires hiring | Flexible |
| Best For | Large enterprises | SMBs and mid-market |
Choosing the Right Outsourced SOC Provider
When evaluating SOC providers, consider:
- 24/7 availability: True round-the-clock coverage, not just monitoring during business hours
- Response times: Sub-15 minute response for critical threats
- Technology stack: Modern EDR/XDR, SIEM, and SOAR capabilities
- Analyst certifications: CISSP, CISM, CEH, GIAC credentials
- Threat intelligence: Access to current threat data and research
- Compliance support: Help meeting GDPR, Cyber Essentials requirements
- Local support: Availability for on-site assistance when needed
Want help putting this in place?
Omega IT can set up the protections this guide covers.
Omega IT: Your Outsourced SOC Partner
At Omega IT, we provide comprehensive outsourced SOC services designed for UK businesses. Our service delivers:
- 24/7/365 security monitoring by certified analysts
- Rapid incident response with sub-15 minute reaction times
- Advanced threat detection using AI and machine learning
- Proactive threat hunting to find hidden attackers
- Continuous analysis of telemetry across your environment
- Regular security reports and recommendations
- UK-wide support combined with global threat intelligence
Get Enterprise Security Without Enterprise Costs
Stop worrying about cyber threats and start benefiting from professional security operations. Contact Omega IT today to learn how our outsourced SOC service can protect your business.
Call us on 0800 254 5458 or visit our contact page for a free security consultation.